
Summary:
Researchers discovered a new threat group going by the name of Anonymous Sudan, which has launched several Distributed Denial of Service (DDoS) attacks against organizations in Sweden, the Netherlands, Australia, and Germany, apparently in retaliation for anti-Muslim activity that had occurred in those nations. There are various clues left behind by Anonymous Sudan that led to the group being connected with Killnet in some way. The main clue is that Killnet has carried out DDoS attacks, which are Anonymous Sudan's main attack vector. Most of the Anonymous Sudan Telegram posts are in Russian, and they target every country that supports Ukraine in its conflict with Russia, which is further circumstantial proof that the group has ties to Russia.[/subscribe_to_unlock_form]
Summary:
Researchers discovered a new threat group going by the name of Anonymous Sudan, which has launched several Distributed Denial of Service (DDoS) attacks against organizations in Sweden, the Netherlands, Australia, and Germany, apparently in retaliation for anti-Muslim activity that had occurred in those nations. There are various clues left behind by Anonymous Sudan that led to the group being connected with Killnet in some way. The main clue is that Killnet has carried out DDoS attacks, which are Anonymous Sudan's main attack vector. Most of the Anonymous Sudan Telegram posts are in Russian, and they target every country that supports Ukraine in its conflict with Russia, which is further circumstantial proof that the group has ties to Russia.[emaillocker id="1283"]
Most of the information regarding Anonymous Sudan can be found on the group's Telegram channel, which was established on January 18, 2023, just days before its initial strike. The group's initial action, in retaliation for the Quran's burning in Stockholm, targeted Swedish governmental and commercial resources. The following day, the group focused on attacks against Dutch government facilities, ostensibly in reprisal for the Quran's burning in the Dutch city of Enschede. France is also a target for Anonymous Sudan, which has threatened to attack it for its anti-Islamic actions. Anonymous Sudan provided data containing emails and passwords as evidence of the Air France attack. In reviewing the emails, researchers discovered that some of them had already been leaked.
The subsequent attack was the first of several to officially connect Killnet to Anonymous Sudan. The incident occurred in late January 2023, and according to the Telegram post, Killnet received assistance from Anonymous Sudan in its attack on the German Federal Intelligence Agency. The second attack carried out in concert with Killnet was directed against PayPal. Anonymous Sudan claimed a successful DDoS attack on the cybersecurity firm Radware’s website. Threats against a wide range of Australian institutions, including airports, universities, and healthcare facilities, were posted on March 24. Anonymous Rasmus Paludan, a political activist with dual Danish and Swedish citizenship, burned the Quran in Denmark, prompting Sudan to declare recently that Denmark is their target. All the aforementioned nations support Ukraine.
Attacks by Anonymous Sudan have the potential to seriously impact government functions as well as those of hospitals and airports. The group has claimed responsibility for several acts and issued threats against a variety of targets. Although Anonymous Sudan's aims and objectives are not entirely apparent, many of their operations frequently resemble attempts to increase public awareness of political and social issues. Since the beginning of the Russian-Ukraine war, this group has claimed to support the Russian cause, and as a result, it frequently attacks Ukrainian targets.
Threat Profile:
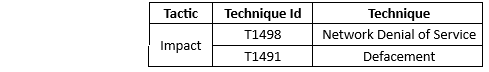
Recommendations:
References:
The following reports contain further technical details:
[/emaillocker]