
Summary:
8220 Gang is a Chinese backed APT group active since 2017 and known for deploying custom cryptominer on Infected hosts. The threat group typically takes advantage of publicly available exploits and brute-force attacks to spread the malware. In its recent campaign, the threat actor is seen exploiting public cloud environments. The threat actor is using, PwnRig a custom crypto miner and kaiten backdoor for deploying additional payload on an infected host.[/subscribe_to_unlock_form]
Summary:
8220 Gang is a Chinese backed APT group active since 2017 and known for deploying custom cryptominer on Infected hosts. The threat group typically takes advantage of publicly available exploits and brute-force attacks to spread the malware. In its recent campaign, the threat actor is seen exploiting public cloud environments. The threat actor is using, PwnRig a custom crypto miner and kaiten backdoor for deploying additional payload on an infected host.[emaillocker id="1283"]
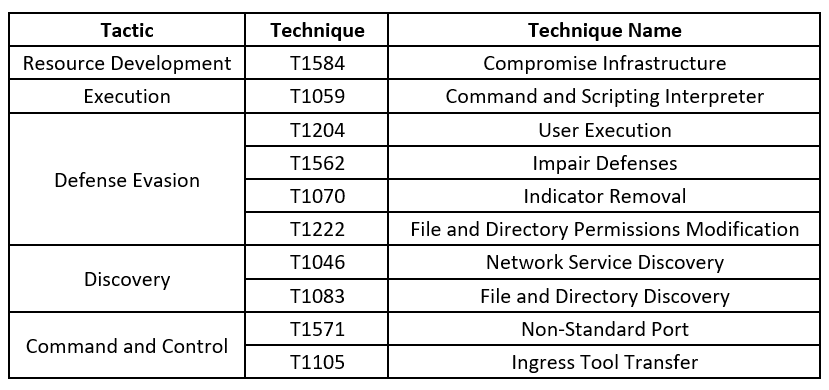
Threat Profile:
References:
The following reports contain further technical details:
[/emaillocker]