
Summary:
Security researchers have discovered a new malware campaign targeting Citrix users. The malware, named AresLoader, is being distributed through a disguised GitLab repository. Once installed, AresLoader can steal sensitive information, including login credentials and system information, from the infected device. The attack begins with a phishing email containing a link to a GitLab repository disguised as a legitimate file-sharing service. The repository contains a malicious PowerShell script, which is designed to download and execute the AresLoader malware. The script is disguised as a benign file, making it difficult to detect by traditional security tools.[/subscribe_to_unlock_form]
Summary:
Security researchers have discovered a new malware campaign targeting Citrix users. The malware, named AresLoader, is being distributed through a disguised GitLab repository. Once installed, AresLoader can steal sensitive information, including login credentials and system information, from the infected device. The attack begins with a phishing email containing a link to a GitLab repository disguised as a legitimate file-sharing service. The repository contains a malicious PowerShell script, which is designed to download and execute the AresLoader malware. The script is disguised as a benign file, making it difficult to detect by traditional security tools.[emaillocker id="1283"]
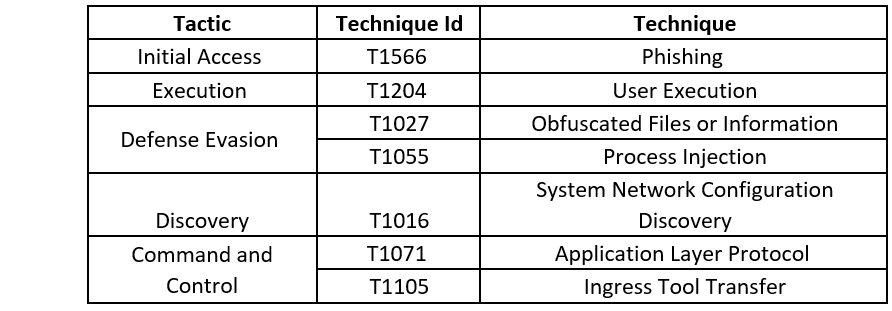
Once the script is executed, it downloads the AresLoader malware from a remote server. The malware is designed to evade detection by using various obfuscation techniques, such as encrypted strings and code obfuscation. AresLoader also uses a technique known as "process hollowing," which involves launching a legitimate process and then replacing its code with the malware. This technique makes it difficult for antivirus software to detect the malware.
AresLoader is a modular malware, which means it can download additional modules and payloads from the attacker's server. The malware can steal sensitive information, such as usernames and passwords, from web browsers, email clients, and other applications. AresLoader can also take screenshots of the infected device and upload them to the attacker's server. The malware is also capable of downloading and executing additional malware payloads, such as ransomware. The attackers can use this capability to launch secondary attacks on the infected device or network. The AresLoader malware is particularly dangerous for Citrix users. Citrix is a popular remote access tool used by many organizations to provide remote access to their employees. AresLoader can steal Citrix login credentials, allowing attackers to gain unauthorized access to sensitive corporate systems and data.
AresLoader is a dangerous malware that can cause significant damage to organizations. It is important for organizations to take proactive steps to protect against this and other malware threats. By implementing best practices for security and leveraging advanced threat detection and response solutions, organizations can reduce their risk of falling victim to cyber attacks.
Threat Profile:
References:
The following reports contain further technical details:
[/emaillocker]