
Summary:
Researchers confirmed that a malware attack in February 2023 led to a number of router infections in Japan GobRAT malware was said to be used in the attack. The attacker's initial target was routers with publicly accessible WEBUI. They exploited vulnerabilities and executed scripts to infect the routers with GobRAT.[/subscribe_to_unlock_form]
Summary:
Researchers confirmed that a malware attack in February 2023 led to a number of router infections in Japan GobRAT malware was said to be used in the attack. The attacker's initial target was routers with publicly accessible WEBUI. They exploited vulnerabilities and executed scripts to infect the routers with GobRAT.[emaillocker id="1283"]
The Loader Script performs the role of a loader and includes features for creating scripts, downloading GobRAT, and creating a backdoor using a hardcoded SSH public key. By registering the Start Script's file path in crontab, the Loader Script also makes use of persistence. GobRAT lacks persistence features, in contrast to the Loader Script. The Daemon Script is created and launched by the Loader Script, which also disables the firewall, downloads GobRAT customised for the target machine's architecture, creates a persistent Start Script, disables the firewall, registers an SSH public key in /root/.ssh/authorized_keys, and creates and runs the Daemon Script.
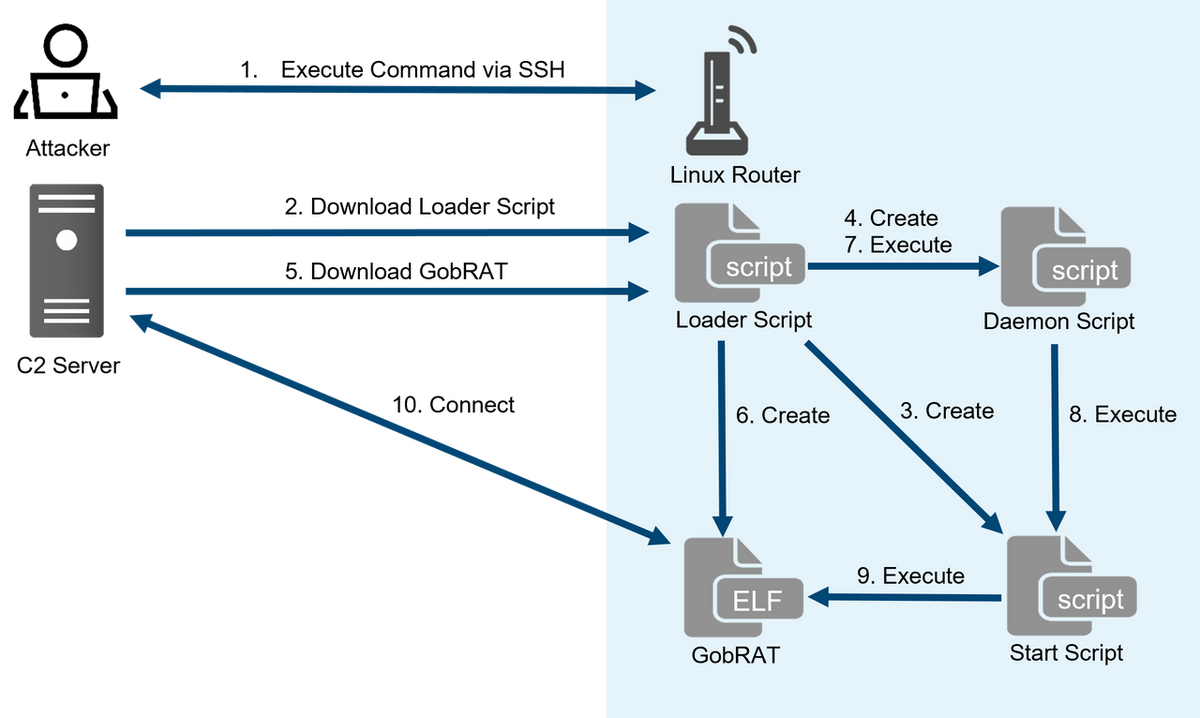
Attack Flow
GobRAT is run by the Start Script's code, and the startup time is recorded in a file called restart.log. Additionally, it uses the filename "apached" to make GobRAT appear to be a genuine process. Every 20 seconds, the Daemon Script checks to see if the Start Script is still active and, if not, restarts it. This feature was probably added as a contingency plan. GobRAT, a RAT (Remote Access Trojan) created in the Go programming language, communicates with a command-and-control (C2) server using TLS (Transport Layer Security) and runs several commands. GobRAT includes UPX version 4 series and supports ARM, MIPS, x86, and x86-64 architectures, among others. When a sample is first started, GobRAT runs checks on it and records data on its IP address, MAC address, uptime, and network communication status.
The analysis of the router infections in Japan reveals the use of GobRAT malware and its sophisticated techniques. The findings highlight the importance of strong security measures, thorough code scrutiny, and the need for robust analysis tools to detect and mitigate the risks of similar supply chain attacks.
Threat Profile:
References:
The following reports contain further technical details:
https://thehackernews.com/2023/05/new-gobrat-remote-access-trojan.html
[/emaillocker]