
Summary:
Researchers recently discovered a cluster of virtualized malware loaders that have joined the trend while investigating recent malvertising (malicious advertising) attacks. The loaders are written in.NET and use virtualization, based on the KoiVM virtualizing protector for.NET applications, to hide their implementation and execution.KoiVM is a ConfuserEx.NET protector plugin that obfuscates a program's opcodes so that only the virtual machine understands them. Among the payloads distributed by MalVirt loaders, researchers discovered infostealer malware of the Formbook family. Formbook and it is newer version XLoader is a feature-rich infostealer malware that includes keylogging, screenshot theft, theft of web and other credentials, and staging of additional malware.[/subscribe_to_unlock_form]
Summary:
Researchers recently discovered a cluster of virtualized malware loaders that have joined the trend while investigating recent malvertising (malicious advertising) attacks. The loaders are written in.NET and use virtualization, based on the KoiVM virtualizing protector for.NET applications, to hide their implementation and execution.KoiVM is a ConfuserEx.NET protector plugin that obfuscates a program's opcodes so that only the virtual machine understands them. Among the payloads distributed by MalVirt loaders, researchers discovered infostealer malware of the Formbook family. Formbook and it is newer version XLoader is a feature-rich infostealer malware that includes keylogging, screenshot theft, theft of web and other credentials, and staging of additional malware.[emaillocker id="1283"]
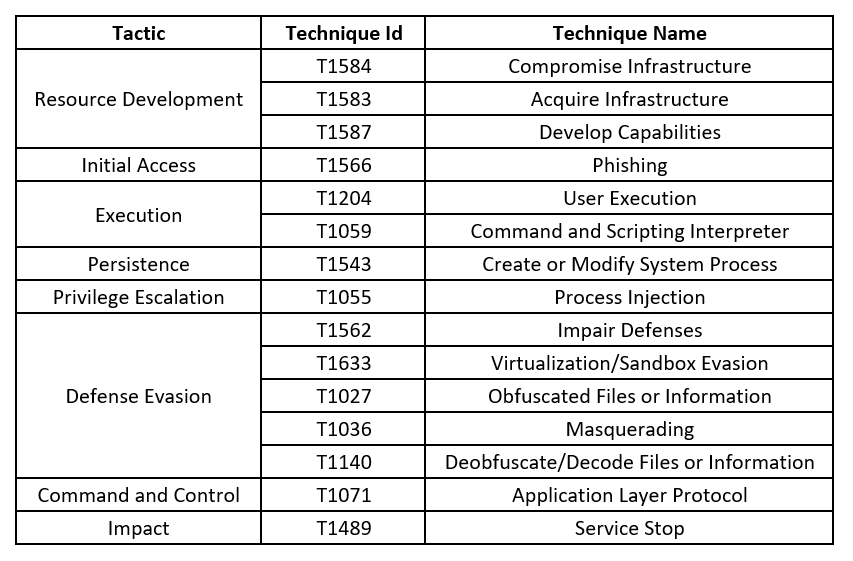
Threat Profile:
References:
The following reports contain further technical details:
[/emaillocker]