
Summary:
GuLoader also known as Cloud Eye is a malware downloader first discovered in December 2019. GuLoader is used by threat actors to deliver various second-stage payloads such as remote access trojans (RAT) and stealers. It infects devices through malicious email attachments. Attackers use phishing emails to deliver the malware as a Visual Basic script. Now, a recently examined sample demonstrates the most modern anti-analysis evasion methods, such as anti-debugging, anti-VM’s, and anti-sandboxing.[/subscribe_to_unlock_form]
Summary:
GuLoader also known as Cloud Eye is a malware downloader first discovered in December 2019. GuLoader is used by threat actors to deliver various second-stage payloads such as remote access trojans (RAT) and stealers. It infects devices through malicious email attachments. Attackers use phishing emails to deliver the malware as a Visual Basic script. Now, a recently examined sample demonstrates the most modern anti-analysis evasion methods, such as anti-debugging, anti-VM’s, and anti-sandboxing.[emaillocker id="1283"]
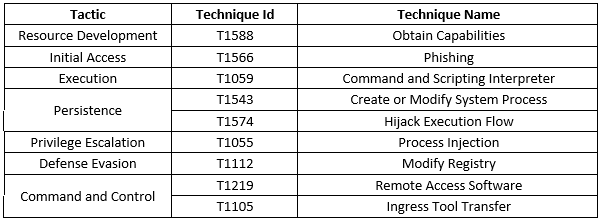
Threat Profile:
References:
The following reports contain further technical details:
https://thehackernews.com/2022/12/guloader-malware-utilizing-new.html
[/emaillocker]