
Summary:
Researchers have discovered a new campaign carried out by TA886, a previously unknown threat actor. The threat actor, first identified in October 2022, uses custom malware called "Screenshotter" to target organizations in the United States and Germany. Phishing emails are used by attackers to deliver malware and gain initial access. The Threat Actor is using Screenshotter to gather information and drop additional payloads in order to gain access to the victim machine and infect it with new malware Rhadamanthys. This malware has the ability to steal credentials, cookies stored in web browsers, and cryptocurrency wallets.[/subscribe_to_unlock_form]
Summary:
Researchers have discovered a new campaign carried out by TA886, a previously unknown threat actor. The threat actor, first identified in October 2022, uses custom malware called "Screenshotter" to target organizations in the United States and Germany. Phishing emails are used by attackers to deliver malware and gain initial access. The Threat Actor is using Screenshotter to gather information and drop additional payloads in order to gain access to the victim machine and infect it with new malware Rhadamanthys. This malware has the ability to steal credentials, cookies stored in web browsers, and cryptocurrency wallets.[emaillocker id="1283"]
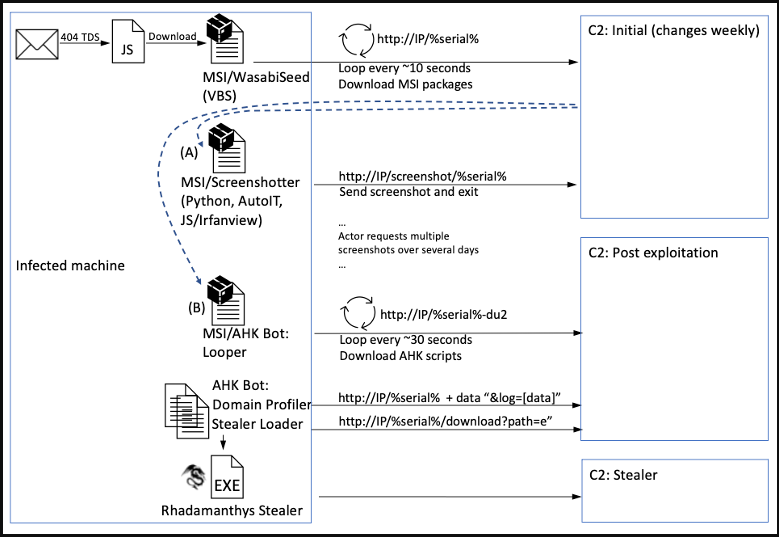
Infection Chain
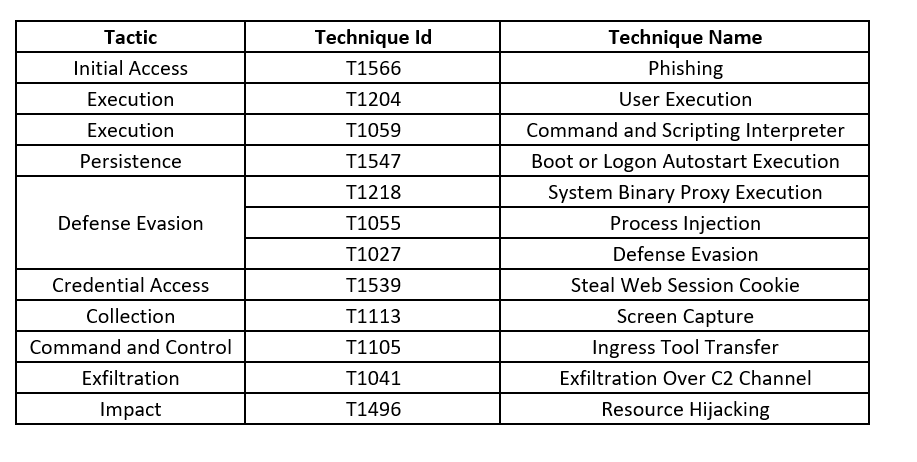
Threat Profile:
References:
The following reports contain further technical details:
[/emaillocker]