
Researchers have spotted a new type of spear-phishing campaign targeting Japanese organizations using Lodeinfo malware. Lodeinfo is a sophisticated fileless malware. Chinese APT group known as Cicada is said to be behind this campaign. Malicious documents and software are used as a lure to target organizations. LODEINFO is under frequent updates, and that multiple functions are been added hence it is difficult to detect.

Infection chain[/subscribe_to_unlock_form]
Researchers have spotted a new type of spear-phishing campaign targeting Japanese organizations using Lodeinfo malware. Lodeinfo is a sophisticated fileless malware. Chinese APT group known as Cicada is said to be behind this campaign. Malicious documents and software are used as a lure to target organizations. LODEINFO is under frequent updates, and that multiple functions are been added hence it is difficult to detect.
Infection chain[emaillocker id="1283"]
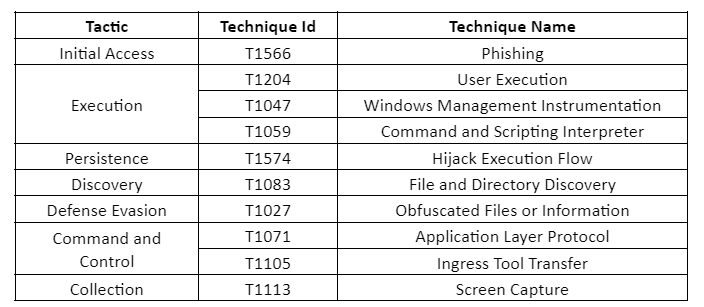
Threat Profile:
References:
The following reports contain further technical details:
(Kindly exclude this link in the advisory mail)
https://securelist.com/apt10-tracking-down-lodeinfo-2022-part-ii/107745/
[/emaillocker]