
Summary:
Organizations in the Spanish-speaking nations of Mexico and Spain are in the crosshairs of a new campaign designed to deliver the Grandoreiro banking trojan. In this campaign, the threat actors impersonate government officials from the Attorney General's Office and from the Public Ministry in the form of spear-phishing emails in order to lure victims to download and execute. Grandoreiro, a prolific banking trojan that has been active since at least 2016, and that specifically targets users in Latin America. The ongoing attacks, which commenced in June 2022, have been observed to target automotive, civil and industrial construction, logistics, and machinery sectors via multiple infection chains in Mexico and chemicals manufacturing industries in Spain. Attack chains entail leveraging spear-phishing emails written in Spanish to trick potential victims into clicking on an embedded link that retrieves a ZIP archive, from which is extracted a loader that masquerades as a PDF document to trigger the execution. The phishing messages prominently incorporate themes revolving around payment refunds, litigation notifications, cancellation of mortgage loans, and deposit vouchers, to activate the infections.[/subscribe_to_unlock_form]
Summary:
Organizations in the Spanish-speaking nations of Mexico and Spain are in the crosshairs of a new campaign designed to deliver the Grandoreiro banking trojan. In this campaign, the threat actors impersonate government officials from the Attorney General's Office and from the Public Ministry in the form of spear-phishing emails in order to lure victims to download and execute. Grandoreiro, a prolific banking trojan that has been active since at least 2016, and that specifically targets users in Latin America. The ongoing attacks, which commenced in June 2022, have been observed to target automotive, civil and industrial construction, logistics, and machinery sectors via multiple infection chains in Mexico and chemicals manufacturing industries in Spain. Attack chains entail leveraging spear-phishing emails written in Spanish to trick potential victims into clicking on an embedded link that retrieves a ZIP archive, from which is extracted a loader that masquerades as a PDF document to trigger the execution. The phishing messages prominently incorporate themes revolving around payment refunds, litigation notifications, cancellation of mortgage loans, and deposit vouchers, to activate the infections.[emaillocker id="1283"]
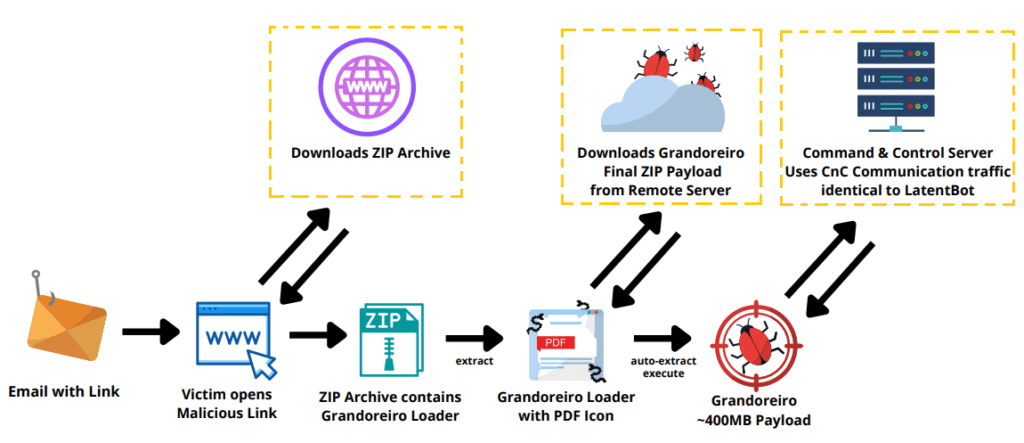
Infection Chain
References:
The following reports contain further technical details:
https://thehackernews.com/2022/08/new-grandoreiro-banking-malware.html
[/emaillocker]