
Summary:
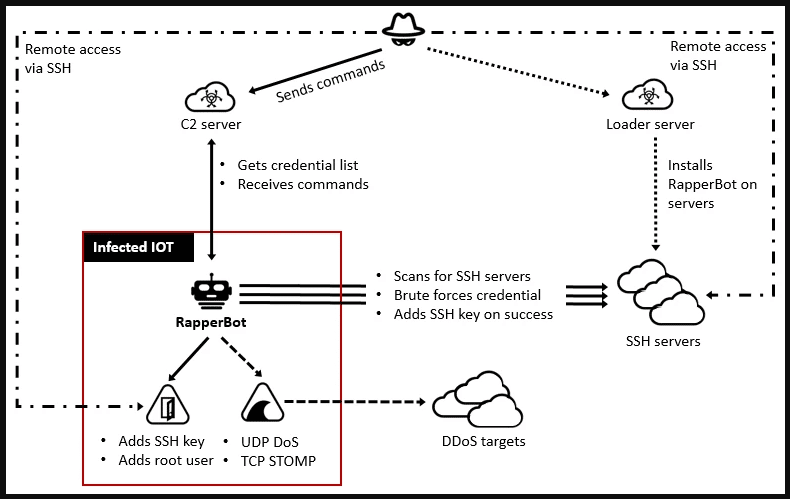
A new botnet called 'RapperBot' is being used in attacks since mid-June 2022, focusing on brute-forcing its way into Linux SSH servers to establish a foothold on the device. The researchers show that RapperBot is based on the Mirai trojan. RapperBot is more tightly controlled, has limited DDoS capabilities, and its operation appears geared towards initial server access, likely to be used as steppingstones for lateral movement within a network. In the most recent samples analysed by the researchers, the bot adds the root user "suhelper" on the compromised endpoints and creates a Cron job that re-adds the user every hour in case an admin discovers the account and deletes it.[/subscribe_to_unlock_form]
Summary:
A new botnet called 'RapperBot' is being used in attacks since mid-June 2022, focusing on brute-forcing its way into Linux SSH servers to establish a foothold on the device. The researchers show that RapperBot is based on the Mirai trojan. RapperBot is more tightly controlled, has limited DDoS capabilities, and its operation appears geared towards initial server access, likely to be used as steppingstones for lateral movement within a network. In the most recent samples analysed by the researchers, the bot adds the root user "suhelper" on the compromised endpoints and creates a Cron job that re-adds the user every hour in case an admin discovers the account and deletes it.[emaillocker id="1283"]
References:
The following reports contain further technical details:
https://www.fortinet.com/blog/threat-research/rapperbot-malware-discovery
[/emaillocker]