
Summary:
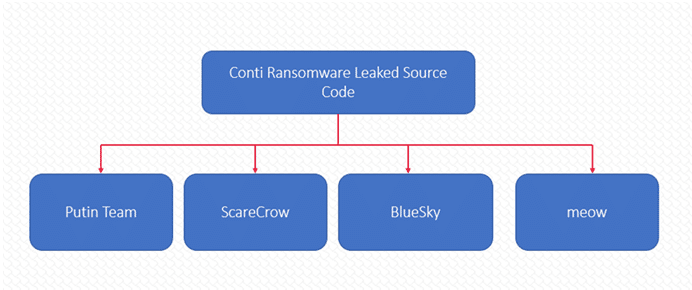
A couple of months back, Ukrainian researchers leaked the Conti ransomware source code. This caused catastrophic consequences for business organizations and consumers, as threat actors exploited the leaked source code to construct their own ransomware operations. some of the ransomware families built from Conti leaked code are Putin Team, ScareCrow, BlueSky, and Meow. Researchers observed that all the ransomware families have a similar infection chain and are mostly operated by Russian-speaking threat groups.[/subscribe_to_unlock_form]
Summary:
A couple of months back, Ukrainian researchers leaked the Conti ransomware source code. This caused catastrophic consequences for business organizations and consumers, as threat actors exploited the leaked source code to construct their own ransomware operations. some of the ransomware families built from Conti leaked code are Putin Team, ScareCrow, BlueSky, and Meow. Researchers observed that all the ransomware families have a similar infection chain and are mostly operated by Russian-speaking threat groups.[emaillocker id="1283"]
Threat Profile:
References:
The following reports contain further technical details:
https://blog.cyble.com/2022/12/22/new-ransomware-strains-emerging-from-leaked-contis-source-code/
[/emaillocker]