
Summary:
First spotted in September 2021, Raspberry Robin is a worm-like malware dropper that sells initial access to compromised networks to ransomware gangs and malware operators. The malware is usually distributed through infected USB drives. It uses autoruns to launch and social engineering to encourage users to click the LNK file masquerading as a legitimate folder to install a malicious payload. The majority of the group's victims are either telecommunications companies or government organizations from the United States, Australia, and Europe.[/subscribe_to_unlock_form]
Summary:
First spotted in September 2021, Raspberry Robin is a worm-like malware dropper that sells initial access to compromised networks to ransomware gangs and malware operators. The malware is usually distributed through infected USB drives. It uses autoruns to launch and social engineering to encourage users to click the LNK file masquerading as a legitimate folder to install a malicious payload. The majority of the group's victims are either telecommunications companies or government organizations from the United States, Australia, and Europe.[emaillocker id="1283"]
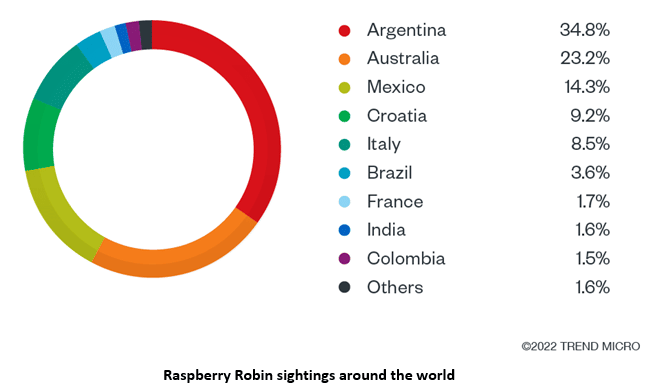
Threat Profile:
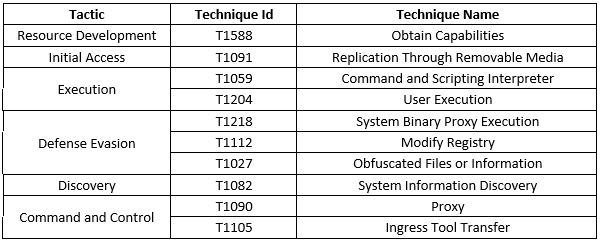
References:
The following reports contain further technical details:
[/emaillocker]