
Summary:
According to researchers cyber criminals are using new version of Raspberry Robin malware to attack Spanish and Portuguese-based financial institutions. Raspberry Robin is a worm-like malware dropper that sells initial access to compromised networks to ransomware gangs and malware operators. The malware is usually distributed through infected USB drives. Researchers stated that new variant of Raspberry Robin began to collect more data about the victims and also found C2 beaconing which use URL with plain-text username and hostname.[/subscribe_to_unlock_form]
Summary:
According to researchers cyber criminals are using new version of Raspberry Robin malware to attack Spanish and Portuguese-based financial institutions. Raspberry Robin is a worm-like malware dropper that sells initial access to compromised networks to ransomware gangs and malware operators. The malware is usually distributed through infected USB drives. Researchers stated that new variant of Raspberry Robin began to collect more data about the victims and also found C2 beaconing which use URL with plain-text username and hostname.[emaillocker id="1283"]
Threat Profile:
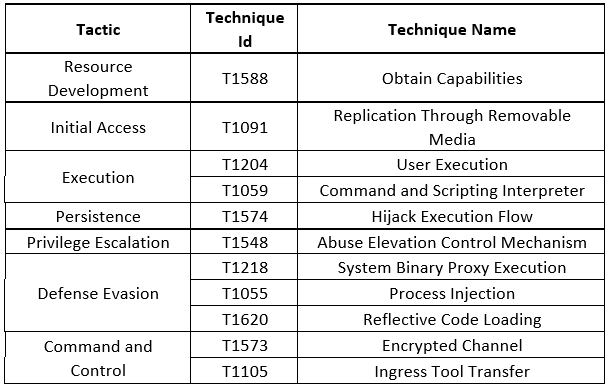
References:
The following reports contain further technical details:
https://www.darkreading.com/threat-intelligence/raspberry-robin-worm-highly-complex-upgrade
[/emaillocker]