
Summary:
Threat Research team provide detailed information about a specific cyber threat involving the APT group called SideCopy. The group has been active since at least 2019 and is believed to align its activities with the goals of the Pakistani government. They have been observed using similar tactics, techniques, and procedures (TTPs) as another Pakistan-based threat actor group known as Transparent Tribe, and there are reports suggesting that SideCopy might be a subsidiary of Transparent Tribe.[/subscribe_to_unlock_form]
Summary:
Threat Research team provide detailed information about a specific cyber threat involving the APT group called SideCopy. The group has been active since at least 2019 and is believed to align its activities with the goals of the Pakistani government. They have been observed using similar tactics, techniques, and procedures (TTPs) as another Pakistan-based threat actor group known as Transparent Tribe, and there are reports suggesting that SideCopy might be a subsidiary of Transparent Tribe.[emaillocker id="1283"]
Researchers highlight an incident where a file referencing an Indian state military research organization and an in-development nuclear missile was discovered. The file was designed to deploy malware associated with the SideCopy APT group. Although the exact initial infection vector is unknown, it is suspected to be a phishing email. Researchers provide insights into a Zip file, named "DRDO-K4-Missile-Clean-room.zip," which likely served as the attachment to the email. Inside the Zip file, three files were found. Two of them, named "office.template.mac" and "office.template.ui," were decoys with no relevance to the infection chain. Their purpose was to make the third file, "DRDO-K4 Missile Clean room.pptx.lnk," appear more legitimate. The .lnk file, a Windows shortcut, didn't immediately open a PowerPoint file as expected. Instead, it leveraged the utility "mshta.exe" to reach out to an attacker-controlled domain.
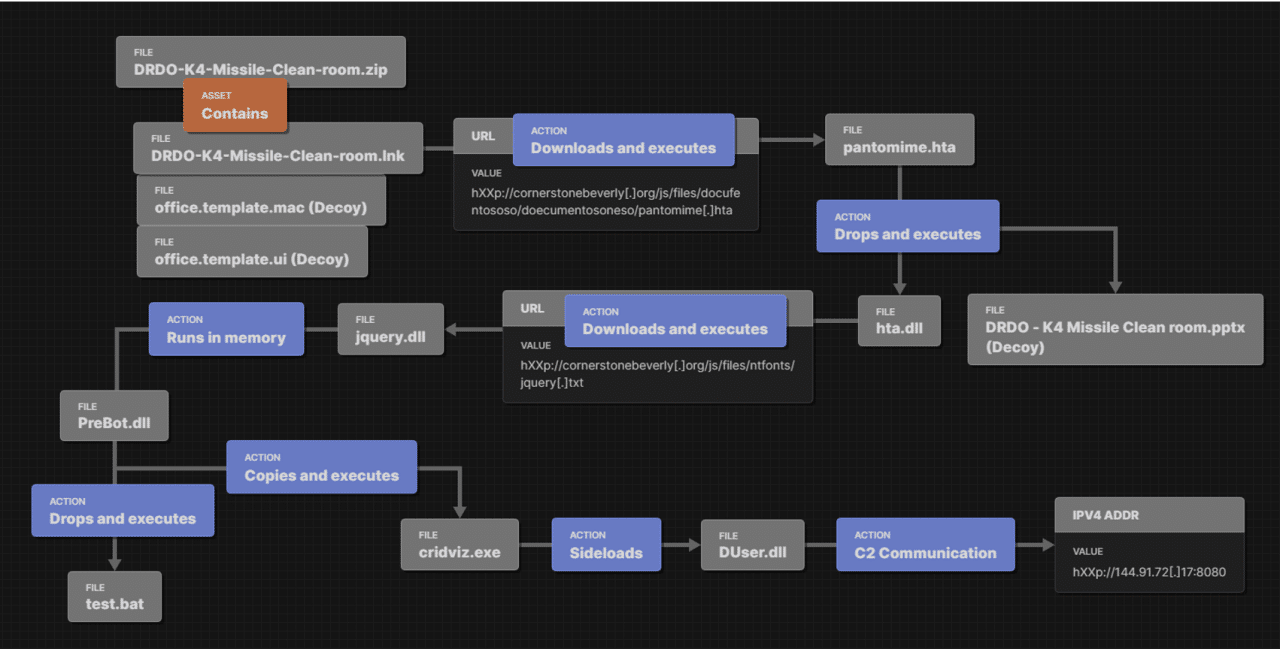
Execution Flow
Researchers explain that previous SideCopy attacks have utilized CACTUSTORCH for obfuscated code deployment, but this campaign seems to differ by employing a tool called SILENTTRINITY. SILENTTRINITY allows the execution of Microsoft .Net code without relying on PowerShell as an intermediary step. The malicious file "Pantomime.hta" was downloaded and executed using this technique. "Pantomime.hta" contains several noteworthy sections. It validates the .Net version on the victim's machine and checks for the existence of a specific folder. It also includes two encoded sections, "dividAndRule" and "punctureTyres," which are base64 encoded. These sections are decoded, deserialized, and executed. The decoded "punctureTyres" section contains a Microsoft .Net library named "hta.dll," which includes the function "RealityShow" used to deploy the file "DRDO-K4 Missile Clean room.pptx" and the next stage of the malware.
After the execution of "Pantomime.hta," the function "openthefile" opens and displays "DRDO-K4 Missile Clean room.pptx." Simultaneously, the function "getThirdStrike" establishes the download location for the file "jquery.hta" and assesses the victim's antivirus situation. The file "jquery.hta" is similar in structure and purpose to "Pantomime.hta" and deploys additional files encoded in variables. Researchers describe the various components and actions of the malware, including the deployment of a Remote Access Trojan (RAT) known as SideCopy. The RAT is loaded into the legitimate application "cridviz.exe" through sideloading. It communicates with a command and control (C2) node and can perform various operations, including starting other processes on the compromised system.
The attack campaign appears to be targeted at individuals within the Indian defense industry, particularly those involved in sensitive projects such as the development of nuclear missiles. The objective is likely to gather intelligence and sensitive information that could be of interest to the Government of Pakistan and other threat actors aligned with their objectives. Overall, this incident highlights the sophistication and persistence of the SideCopy APT group and underscores the importance of robust cybersecurity measures, including email security, endpoint protection, and network monitoring, to defend against such targeted attacks.
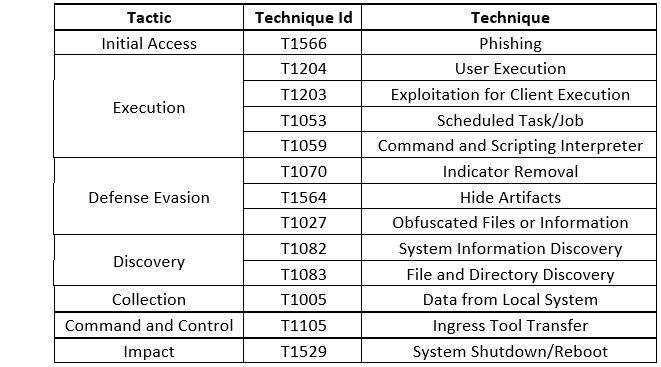
Threat Profile:
References:
The following reports contain further technical details:
https://thehackernews.com/2023/05/sidecopy-using-action-rat-and-allakore.html
[/emaillocker]