
Summary:
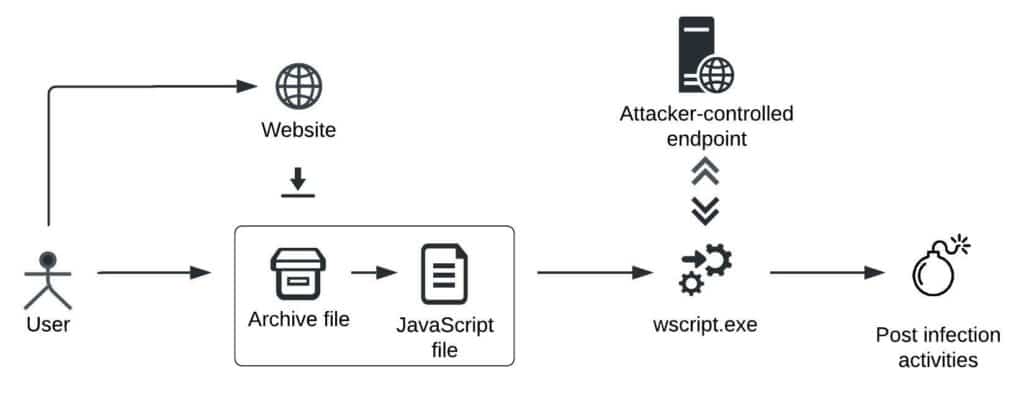
SocGholish is an initial access threat that leverages drive-by-downloads masquerading as software updates, the term Soc in the SocGholish framework refers to the attacker’s use of social engineering to deploy malware on the system. In recent times security researchers have seen a significant increase in Socgholish malware incidents. Socgholish is a loader-type malware that can perform reconnaissance activity and deploy secondary payloads, including Cobalt Strike.[/subscribe_to_unlock_form]
Summary:
SocGholish is an initial access threat that leverages drive-by-downloads masquerading as software updates, the term Soc in the SocGholish framework refers to the attacker’s use of social engineering to deploy malware on the system. In recent times security researchers have seen a significant increase in Socgholish malware incidents. Socgholish is a loader-type malware that can perform reconnaissance activity and deploy secondary payloads, including Cobalt Strike.[emaillocker id="1283"]
Zloader is a popular banking trojan first discovered in 2016 and an improvement from the Zeus trojan, it is designed to steal cookies, passwords, and sensitive information. The main audience of this piece of malware are financial institutions worldwide. Researchers have observed malicious actors distributing Zloader to systems through malicious websites that have masqueraded the malware as an installer of popular applications.
References:
The following reports contain further technical details:
[/emaillocker]