
Summary:
A new ransomware named Somnia is spotted in the wild targeting Ukrainian organizations. The threat group called z-team (UAC-0118) is said to be responsible for these attacks. The main motive of the attacker is to disrupt the operations of the organizations it is targeting, as there is no ransom note or ransom demand. After analysis, it was discovered that the threat actor is using a fake advanced IP scanner software installer, which is a vidar stealer malware to infect the system. It steals victims’ session data to take control of their Telegram accounts and to transfer VPN configuration files. Once inside, the attacker starts data exfiltration using reclone program and drops the cobalt strike beacon.[/subscribe_to_unlock_form]
Summary:
A new ransomware named Somnia is spotted in the wild targeting Ukrainian organizations. The threat group called z-team (UAC-0118) is said to be responsible for these attacks. The main motive of the attacker is to disrupt the operations of the organizations it is targeting, as there is no ransom note or ransom demand. After analysis, it was discovered that the threat actor is using a fake advanced IP scanner software installer, which is a vidar stealer malware to infect the system. It steals victims’ session data to take control of their Telegram accounts and to transfer VPN configuration files. Once inside, the attacker starts data exfiltration using reclone program and drops the cobalt strike beacon.[emaillocker id="1283"]
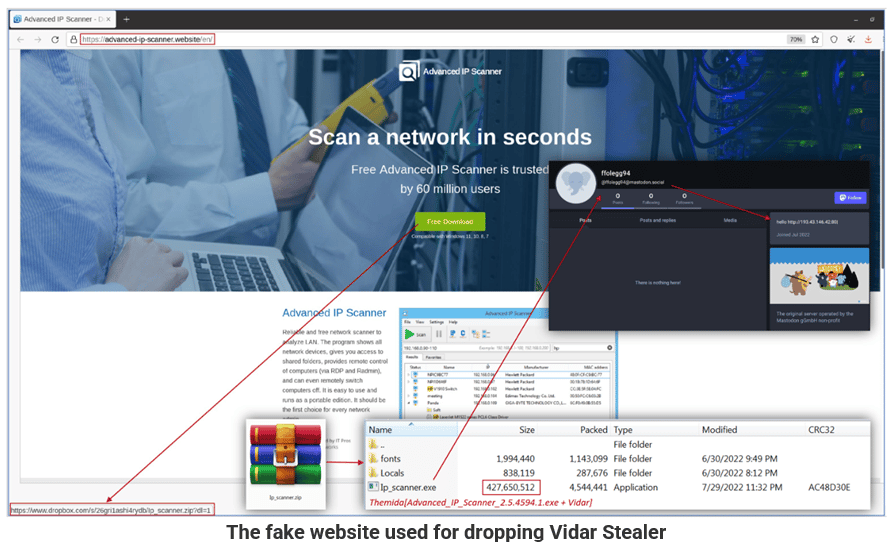
The fake website used for dropping Vidar Stealer
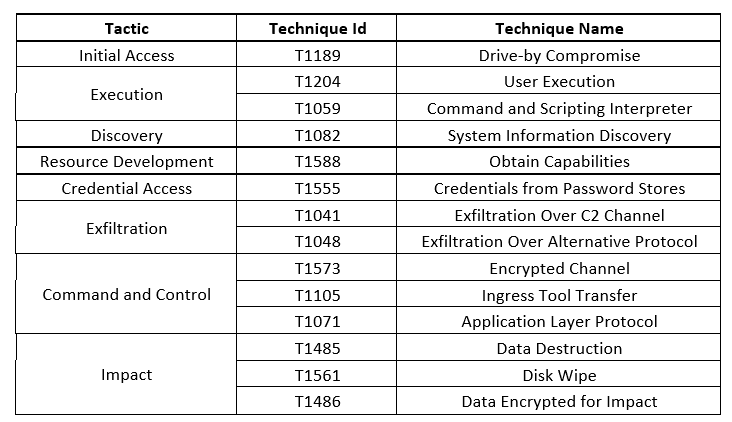
Threat Profile:
References:
The following reports contain further technical details:
(Kindly exclude this link in the advisory mail)
[/emaillocker]