
Summary:
ViperSoftX is a type of malware that steals information, with a particular focus on cryptocurrencies. In 2022, it made headlines for its unique method of hiding malicious code inside log files. This new version of the malware uses DLL sideloading for its arrival and execution techniques and has a more sophisticated encryption method of byte remapping, making decryption and analysis of the shellcode more challenging for analysts. The command-and-control server also changes monthly.[/subscribe_to_unlock_form]
Summary:
ViperSoftX is a type of malware that steals information, with a particular focus on cryptocurrencies. In 2022, it made headlines for its unique method of hiding malicious code inside log files. This new version of the malware uses DLL sideloading for its arrival and execution techniques and has a more sophisticated encryption method of byte remapping, making decryption and analysis of the shellcode more challenging for analysts. The command-and-control server also changes monthly.[emaillocker id="1283"]
Consumer and enterprise sectors have fallen victim to ViperSoftX, with Australia, Japan, and the United States being the top three countries affected in the consumer category. The enterprise sector is primarily based in Southeast Asia Malicious actors behind ViperSoftX use multimedia editors or video format converters, cryptocurrency coin miner apps, phone-related desktop apps, and system cleaner apps. The malware arrives as a package of the carrier executable and the decryptor/loader DLL, typically downloaded from the websites or torrents of (illegal) software solutions. Once the software executables have been included and run in the system, the malicious routine starts.
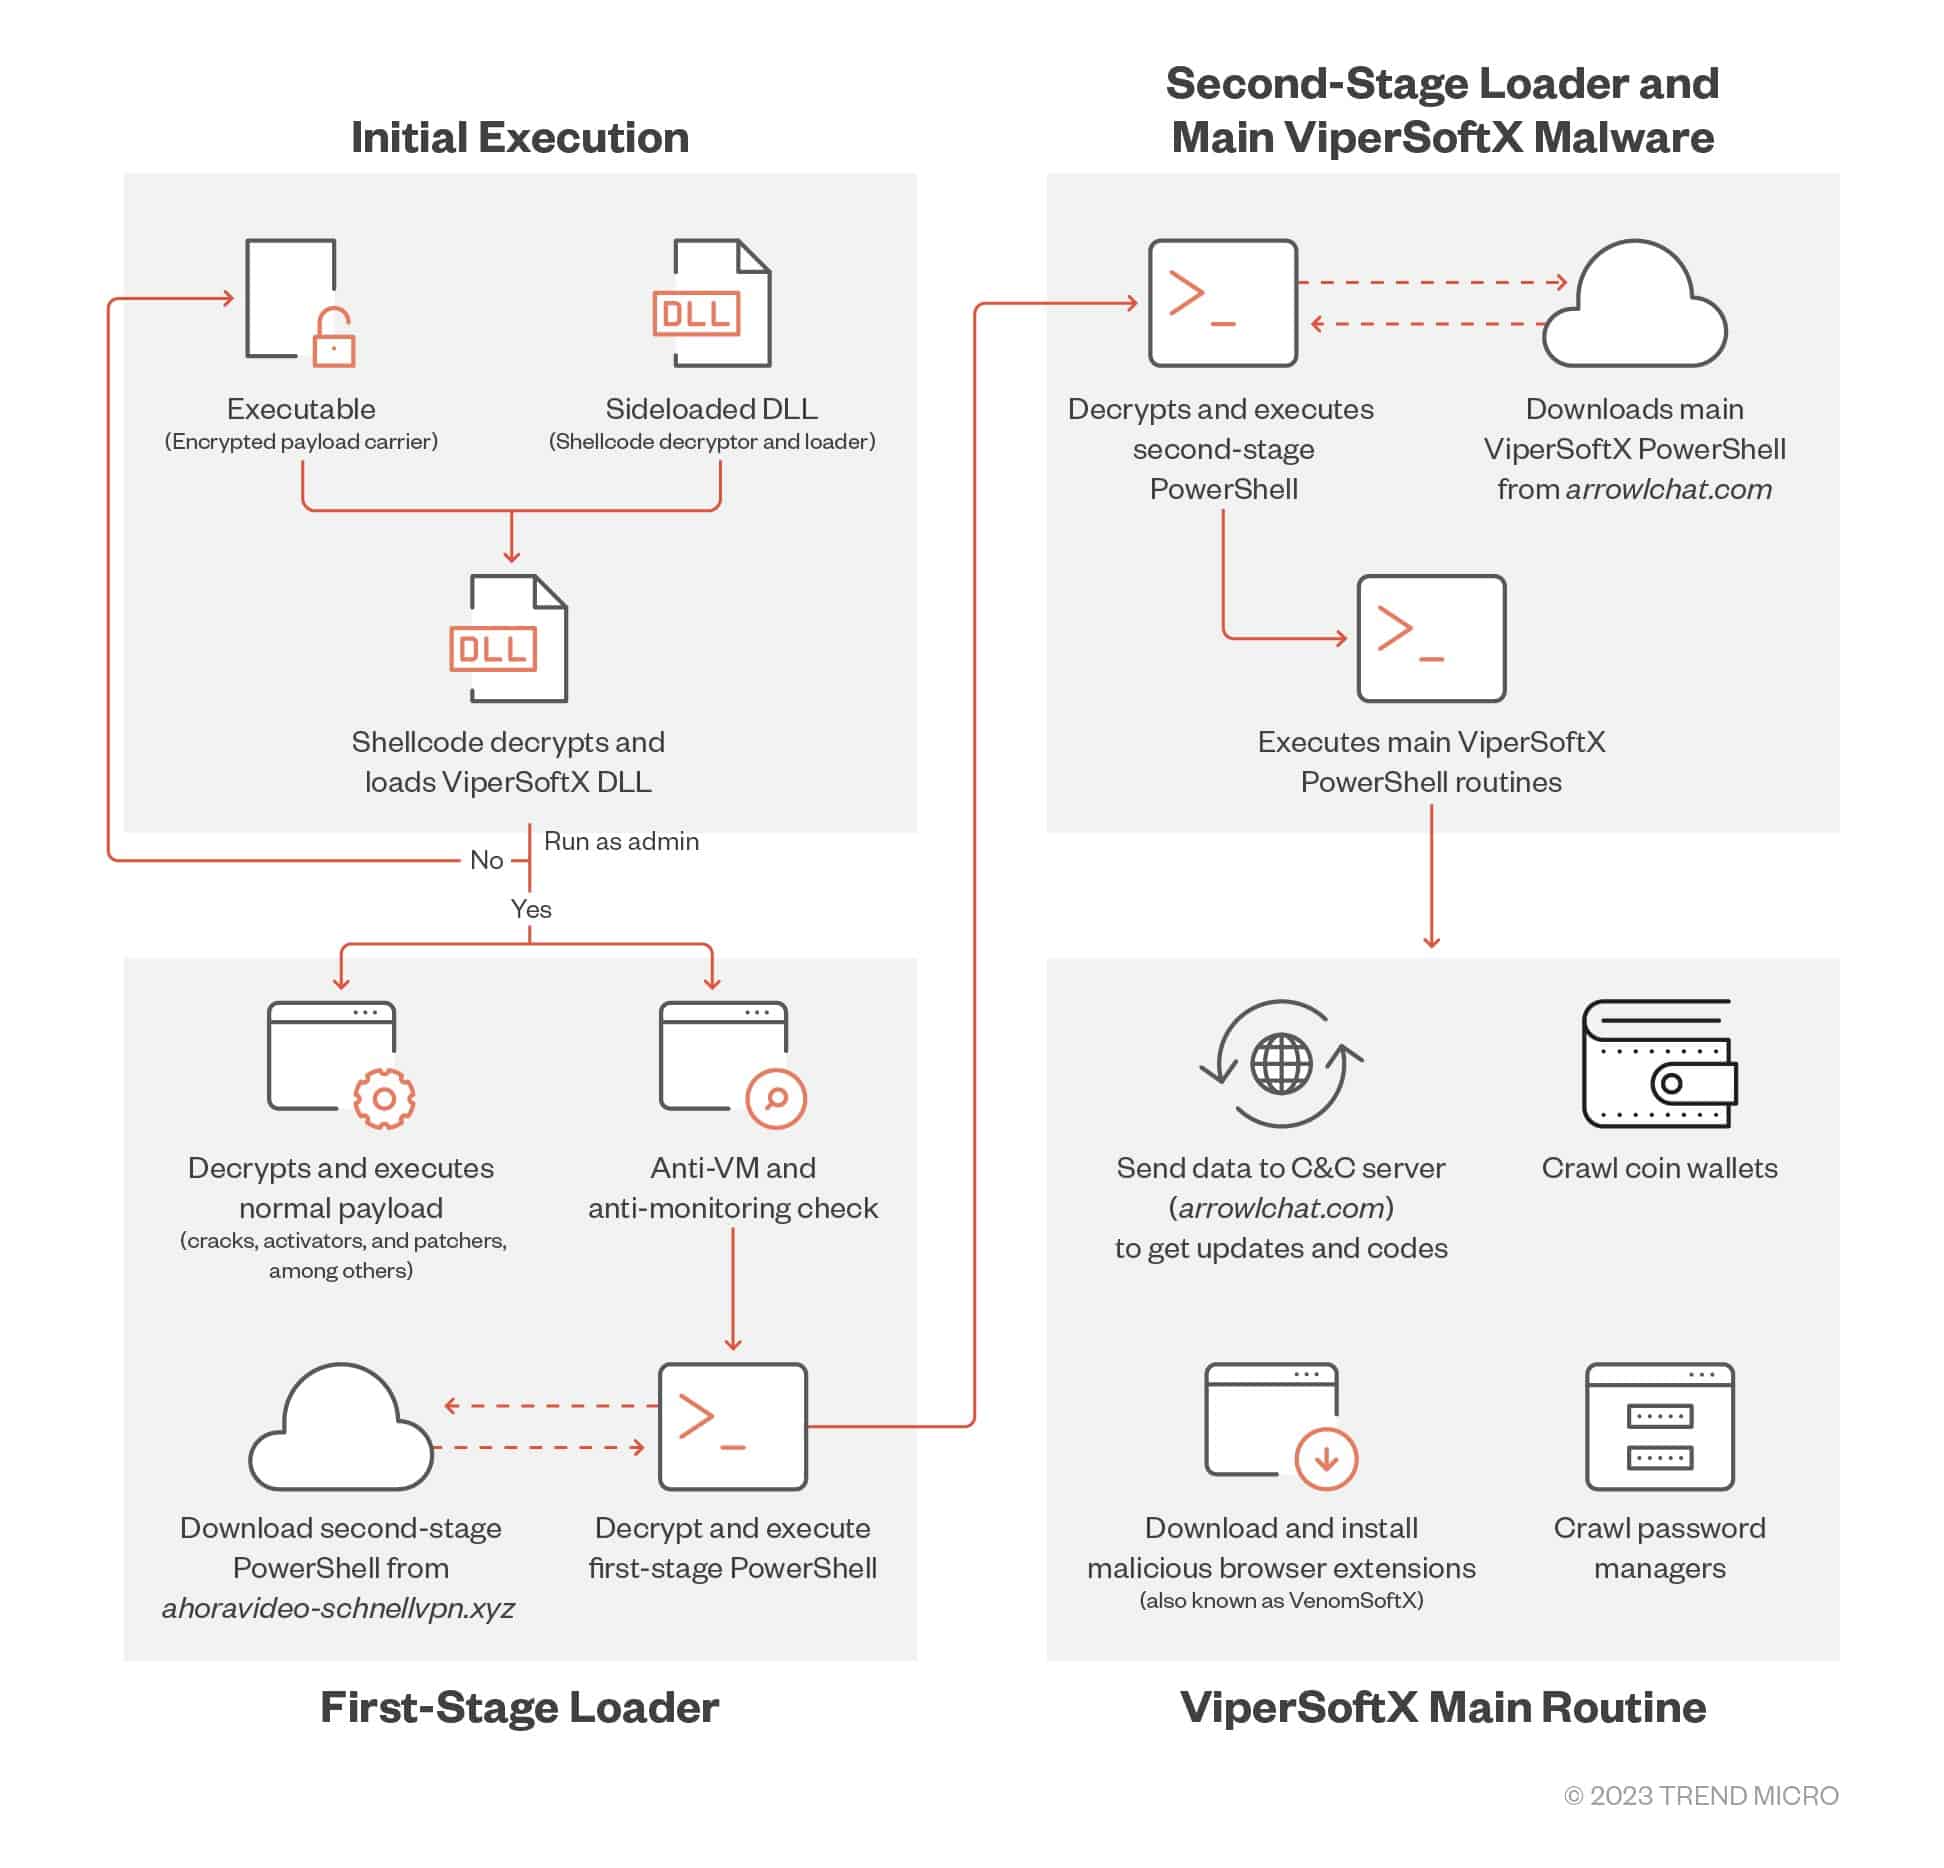
Execution flow of ViperSoftX
ViperSoftX checks for virtualization strings and monitoring tools to check if the system is running a virtual machine (VM). If all checks pass, the malware proceeds to decrypt the PowerShell code and start downloading the main ViperSoftX routine. The byte remapping technique is used to ensure that the shellcode cannot be easily decrypted without the correct byte map, providing some level of protection against forced decryption.
Although known primarily as a cryptocurrency stealer, ViperSoftX can check for a few password managers and uses basic anti-C&C analyses by disallowing communications using web browsers. It still downloads a PowerShell code to crawl through different paths in the system for cryptocurrency wallets. In countries. ViperSoftX typically arrives as a software crack, an activator or a patcher, or a key generator. Cybercriminals often pose malware as a keygen or an activator, and ViperSoftX uses non-malicious software to hide and pose as typical illegal software versions.
ViperSoftX is a dangerous malware that has affected both the consumer and enterprise sectors. It arrives as non-malicious software to deceive users and uses advanced techniques to avoid detection. Its byte remapping technique makes it challenging for analysts to decrypt its shellcode, and it targets not only cryptocurrencies but also password managers. The enterprise sector is a significant target for ViperSoftX, with Australia, Japan, and the US being the leading countries affected.
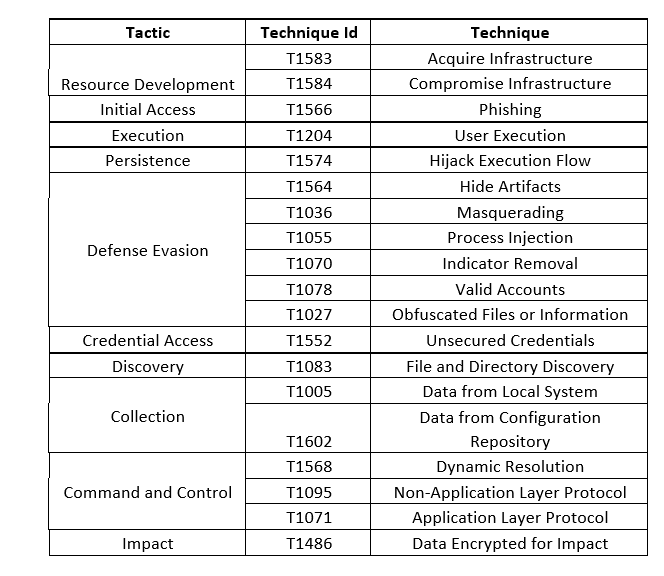
Threat Profile:
References:
The following reports contain further technical details:
https://www.trendmicro.com/en_us/research/23/d/vipersoftx-updates-encryption-steals-data.html
[/emaillocker]