
Summary:
The Abyss Locker ransomware has emerged as a significant threat to both Microsoft Windows and Linux systems, affecting users across various regions globally. Stemming from the HelloKitty ransomware source code, Abyss Locker has evolved with multiple variants targeting different platforms. This edition of the Ransomware Roundup delves into the characteristics and impact of Abyss Locker, shedding light on its infection vectors, victimology, attack methods, and the measures it employs to evade detection. Furthermore, it explores the severity of its consequences and the challenges it poses to affected parties.[/subscribe_to_unlock_form]
Summary:
The Abyss Locker ransomware has emerged as a significant threat to both Microsoft Windows and Linux systems, affecting users across various regions globally. Stemming from the HelloKitty ransomware source code, Abyss Locker has evolved with multiple variants targeting different platforms. This edition of the Ransomware Roundup delves into the characteristics and impact of Abyss Locker, shedding light on its infection vectors, victimology, attack methods, and the measures it employs to evade detection. Furthermore, it explores the severity of its consequences and the challenges it poses to affected parties.[emaillocker id="1283"]
Abyss Locker ransomware manifests in distinct forms for Windows and Linux platforms, each with its own set of functionalities and attack strategies. For Windows systems, the ransomware initiates a series of actions, including service termination, process termination, deletion of Volume Shadow Copies, and encryption of files with a specific extension. It alters desktop wallpapers, drops ransom notes, and utilizes TOR sites for ransom negotiations. Meanwhile, the Linux variant exhibits a different modus operandi, executing run commands, encrypting files with a different extension, and generating ransom notes. Despite variations between versions, the core functionality remains consistent across Abyss Locker iterations. Moreover, while data leak sites have been reported in the past, current observations suggest a focus on ransom negotiations rather than data exposure.
The Abyss Locker ransomware poses a high-severity threat to organizations and individuals, exploiting vulnerabilities in both Windows and Linux environments. Its ability to steal and encrypt sensitive data underscores the urgency of robust cybersecurity measures. The ransomware landscape continues to evolve, proactive defense mechanisms and heightened cybersecurity awareness are essential for mitigating the risks posed by Abyss Locker and similar threats.
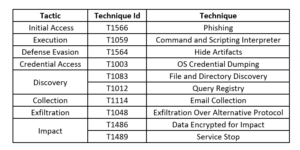
Threat Profile:
References:
The following reports contain further technical details:
https://www.fortinet.com/blog/threat-research/ransomware-roundup-abyss-locker
[/emaillocker]