
Summary:
A newly identified Apple macOS backdoor, named SpectralBlur, has been uncovered by cybersecurity researchers. This backdoor exhibits similarities with the KANDYKORN malware family associated with North Korean threat actors. SpectralBlur is a moderately capable backdoor, enabling file upload/download, shell execution, configuration updates, file deletion, hibernation, or sleep, controlled by commands from a command-and-control server. The overlap with KANDYKORN, known for its advanced remote access trojan capabilities, suggests a potential connection between the two, pointing to the evolving tactics of North Korean threat actors targeting macOS.[/subscribe_to_unlock_form]
Summary:
A newly identified Apple macOS backdoor, named SpectralBlur, has been uncovered by cybersecurity researchers. This backdoor exhibits similarities with the KANDYKORN malware family associated with North Korean threat actors. SpectralBlur is a moderately capable backdoor, enabling file upload/download, shell execution, configuration updates, file deletion, hibernation, or sleep, controlled by commands from a command-and-control server. The overlap with KANDYKORN, known for its advanced remote access trojan capabilities, suggests a potential connection between the two, pointing to the evolving tactics of North Korean threat actors targeting macOS.[emaillocker id="1283"]
SpectralBlur, the newly discovered Apple macOS backdoor, exhibits a range of capabilities that make it a significant cybersecurity concern. Functionally overlapping with the KANDYKORN malware family, it serves as a moderately capable backdoor, allowing threat actors to perform various malicious activities on compromised systems. These capabilities provide threat actors with a toolkit for stealthy and persistent access to macOS systems. One notable aspect of SpectralBlur’s design is its effort to hinder analysis and evade detection. The malware employs the grantpt function to establish a pseudo-terminal, providing a mechanism for executing shell commands received from the command-and-control (C2) server. This tactic enhances the backdoor’s ability to operate covertly and avoid detection by traditional security measures. The use of evasion techniques highlights the sophistication of the threat actor behind SpectralBlur, indicating a deliberate strategy to maintain a persistent presence on family compromised macOS systems. The overlap with the KANDYKORN malware suggests potential connections or shared development requirements between the two, adding a layer of complexity to the threat landscape.
The identification of SpectralBlur underscores the persistent threat posed by North Korean actors targeting macOS, reflecting an uptick in macOS-specific malware discoveries. The overlap with KANDYKORN and the integration of different infection chains reveal the adaptability and evolving tactics of these threat actors. As macOS gains popularity, especially in enterprise settings, the cybersecurity landscape anticipates a surge in new macOS malware variants in the coming year. Security measures need to evolve to counter these emerging threats effectively.
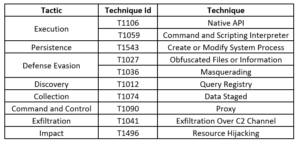
Threat Profile:
References:
The following reports contain further technical details:
https://thehackernews.com/2024/01/spectralblur-new-macos-backdoor-threat.html
[/emaillocker]