
Summary:
Researchers highlighted the activities of a China-linked threat actor known as Earth Lusca. Since then, Earth Lusca has continued its operations and expanded its reach, targeting various countries in the first half of 2023. Researchers uncovered an encrypted file named SprySOCKS, a Linux-targeted backdoor derived from the open-source Windows backdoor Trochilus. This variant showcased new developments, including version differences and similarities to the RedLeaves backdoor.[/subscribe_to_unlock_form]
Summary:
Researchers highlighted the activities of a China-linked threat actor known as Earth Lusca. Since then, Earth Lusca has continued its operations and expanded its reach, targeting various countries in the first half of 2023. Researchers uncovered an encrypted file named SprySOCKS, a Linux-targeted backdoor derived from the open-source Windows backdoor Trochilus. This variant showcased new developments, including version differences and similarities to the RedLeaves backdoor.[emaillocker id="1283"]
The core payload and loader of the SprySOCKS backdoor are both encrypted. The Linux ELF injector, known as "mandibule," served as the foundation for the loader. This injector was altered by the threat actor to load and decode the SprySOCKS second stage. Debug messages left in the code show a lack of skill in development, and the loader even uses the process name "kworker" to hide its activities. The HP-Socket project was used to statically compile the second stage of SprySOCKS, which has a hard-coded AES-ECB password for communication encryption. Additionally hard-coded are the C&C address and port, and communication uses particular header values over TCP. Standard commands for gathering system data, generating an interactive shell, identifying network connections, setting up a SOCKS proxy, and operating on files are all part of the backdoor's capability. Client data and communication closely mirror the malware used by Trochilus and RedLeaves, indicating possible inspiration or source code access.
With a particular emphasis on government agencies involved in foreign affairs, technology, and telecommunications in numerous locations, Earth Lusca has continued its cyber activities. Cobalt Strike and the Linux version of Winnti are only a couple of the tools the threat actor uses to conduct espionage operations while exploiting server vulnerabilities. Organizations must proactively manage their attack surfaces, consistently install patches, and use cutting-edge security tools to protect themselves from such threats.
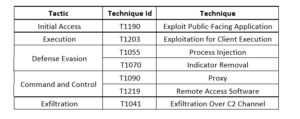
Threat Profile:
References:
The following reports contain further technical details:
[/emaillocker]