
Summary:
A recent security threat has come to light involving a series of malicious packages found on the npm public repository since the beginning of August. These packages have been identified as containing Luna Grabber, an open-source malware designed to steal information, in an attack reminiscent of a similar incident uncovered two years ago. This campaign began in early August, with the first malicious package appearing on August 1. Additional malicious packages, such as noblox.js-ssh and noblox.js-secure, were also discovered. noblox.js-ssh has been reported to npm maintainers, while noblox.js-secure has been removed from npm, likely by its author. The primary targets of this campaign are developers who create scripts for the Roblox gaming platform. Legitimate packages like noblox.js facilitate the creation of scripts that interact with the Roblox website using JavaScript. However, the malicious packages found by researchers mimic the legitimate package by replicating its code and introducing malicious information-stealing functions. This isn't the first time attackers have targeted noblox.js users. A similar campaign was uncovered two years ago, involving malicious npm packages that mimicked noblox.js and delivered ransomware to unsuspecting developers.[/subscribe_to_unlock_form]
Summary:
A recent security threat has come to light involving a series of malicious packages found on the npm public repository since the beginning of August. These packages have been identified as containing Luna Grabber, an open-source malware designed to steal information, in an attack reminiscent of a similar incident uncovered two years ago. This campaign began in early August, with the first malicious package appearing on August 1. Additional malicious packages, such as noblox.js-ssh and noblox.js-secure, were also discovered. noblox.js-ssh has been reported to npm maintainers, while noblox.js-secure has been removed from npm, likely by its author. The primary targets of this campaign are developers who create scripts for the Roblox gaming platform. Legitimate packages like noblox.js facilitate the creation of scripts that interact with the Roblox website using JavaScript. However, the malicious packages found by researchers mimic the legitimate package by replicating its code and introducing malicious information-stealing functions. This isn't the first time attackers have targeted noblox.js users. A similar campaign was uncovered two years ago, involving malicious npm packages that mimicked noblox.js and delivered ransomware to unsuspecting developers.[emaillocker id="1283"]
In this recent campaign, the malicious payload differs from the previous one. It includes a PyInstaller-compiled executable that installs Luna Grabber, a malware designed to steal information from web browsers, Discord applications, and local system data. It's not uncommon for researchers to find multistage malware on public repositories, but such cases are less frequent on npm. The discovery of this campaign was the result of routine monitoring and package scanning, with the initial suspicious package, noblox.js-vps, standing out due to its typosquatting on the legitimate noblox.js package. Upon inspection, researchers found several suspicious behaviors within noblox.js-vps, including command execution, information enumeration, and event monitoring. These are common indicators of malicious packages on open-source repositories. The attackers behind noblox.js-vps put significant effort into making their package appear legitimate. The package closely resembled the official noblox.js GitHub page, with the only difference being the inclusion of a separate file, postinstall.js, containing the malicious payload.
This malicious script checks if it's running on a Windows machine and, if so, downloads and executes a second-stage malicious script from Discord CDN. Subsequent versions of noblox.js-vps included obfuscated code in the postinstall.js script. The third-stage executable payload, which all second-stage scripts attempted to fetch, was identified as a PyInstaller-compiled executable serving Luna Grabber. Luna Grabber is designed to steal information from web browsers, Discord applications, and local systems. It possesses features common in malicious software, including the ability to detect virtual environments and self-destruct. The attackers leveraged Luna Grabber's user-friendly builder application to create the executable served by the malicious packages. This builder simplifies the process of configuring the malware, allowing the attacker to select options such as "Add to Startup," "Ping," and "Injection," as well as collect information about the system.
Additional packages in this campaign, like noblox.js-ssh and noblox.js-secure, followed a similar pattern, with malicious code in postinstall.js scripts downloading second-stage payload scripts. Unfortunately, the third stage wasn't retrievable at the time of the report. Fortunately, the impact of this campaign was limited due to its short duration. The combined downloads of the three malicious packages were under 1,000, with noblox.js-vps being the most downloaded, at 585. Nonetheless, it's crucial for developers to remain vigilant and exercise caution when downloading packages from public repositories.
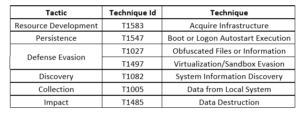
Threat Profile:
References:
The following reports contain further technical details:
https://thehackernews.com/2023/08/over-dozen-malicious-npm-packages.html
[/emaillocker]