
Summary:
Parrot TDS, a traffic direction system, has been identified as a significant and evolving threat since its public reporting in October 2021. This system injects malicious scripts into existing JavaScript code on compromised servers, posing a threat to millions of potential victims. The uniqueness of Parrot TDS lies in its identifiable keywords, such as Ndsj, Ndsw, and Ndsx, consistently used in injected JavaScript. The campaign, active since at least 2019, has gained attention for its longevity and wide-ranging impact.[/subscribe_to_unlock_form]
Summary:
Parrot TDS, a traffic direction system, has been identified as a significant and evolving threat since its public reporting in October 2021. This system injects malicious scripts into existing JavaScript code on compromised servers, posing a threat to millions of potential victims. The uniqueness of Parrot TDS lies in its identifiable keywords, such as Ndsj, Ndsw, and Ndsx, consistently used in injected JavaScript. The campaign, active since at least 2019, has gained attention for its longevity and wide-ranging impact.[emaillocker id="1283"]
Parrot TDS consists of two main components: landing scripts and payload scripts. Landing scripts, with versions labeled V1 to V4, are injected into existing JavaScript files on compromised servers. These scripts conduct environment checks and, if conditions are met, lead the victim's browser to query a payload server. The payload scripts, identified with the keyword Ndsx, are responsible for directing the victim's browser to a malicious location or content. The landing scripts have evolved over time, with increased obfuscation and changes in functionality. The campaign targets servers worldwide, compromising websites through various versions of injected JavaScript. The scripts are often found in websites using CMS like WordPress or Joomla, showcasing the attackers' use of automatic tools to exploit known vulnerabilities.
Parrot TDS represents a persistent and evolving threat landscape, with a campaign spanning over four years and demonstrating continuous adaptation with new techniques and obfuscations. The attack targets a diverse range of victims globally, indicating that the threat actors exploit vulnerabilities across industries, nationalities, and geographic areas. Website administrators are urged to remain vigilant by searching server content for keywords associated with Parrot TDS and conducting audits to identify any extra files on web servers. The insights provided by researchers contribute to the understanding of Parrot TDS and assist in developing strategies for detection and mitigation against this long-standing threat.
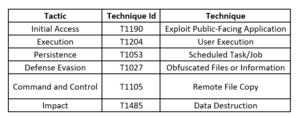
Threat Profile:
References:
The following reports contain further technical details:
[/emaillocker]