
Summary:
Researchers have recently disclosed a critical advisory pertaining to CVE-2023-46604, highlighting Apache's vulnerability linked to the deserialization of untrusted data. Exploiting this vulnerability, threat actors are exploiting a newfound Golang-based botnet termed GoTitan, in tandem with a .NET program named "PrCtrl Rat." These malicious tools exhibit alarming capabilities for remote control, showcasing the severity and the continuously evolving nature of this identified vulnerability.[/subscribe_to_unlock_form]
Summary:
Researchers have recently disclosed a critical advisory pertaining to CVE-2023-46604, highlighting Apache's vulnerability linked to the deserialization of untrusted data. Exploiting this vulnerability, threat actors are exploiting a newfound Golang-based botnet termed GoTitan, in tandem with a .NET program named "PrCtrl Rat." These malicious tools exhibit alarming capabilities for remote control, showcasing the severity and the continuously evolving nature of this identified vulnerability.[emaillocker id="1283"]
Exploitation of CVE-2023-46604 involves an intricate process where threat actors leverage the OpenWire protocol, often on port 61616, to trigger the system's unmarshalling of a controlled class. This action prompts vulnerable servers to retrieve a specific class configuration XML file from an external URL provided by the attacker. GoTitan, written in the Go programming language and available as x64 binaries, exhibits early-stage development traits. It self-replicates, establishes recurring executions via cron, and initiates data collection on compromised endpoints, transmitting crucial system information to its Command and Control (C2) server. GoTitan communicates via a hardcoded string and supports ten distinct DDoS attack methods. Moreover, threat actors utilize tools like Sliver to compromise multiple targets across diverse platforms and architectures. Sliver facilitates the creation of customized implants, enabling command execution, file manipulation, and evasion of detection through various encoders. Despite a patch released over a month ago, threat actors persist in exploiting CVE-2023-46604, perpetuating the distribution of malware via vulnerable servers.
Notably, the emergence of GoTitan, PrCtrl Rat, and the ongoing exploits by Sliver, Kinsing, and Ddostf signify the persistent and evolving threat landscape surrounding this vulnerability. Considering these developments, vigilance remains paramount. Organizations must prioritize regular system updates, patching, and continuous monitoring of security advisories. Mitigating the risk of exploitation necessitates a proactive approach, considering the evolving tactics of threat actors leveraging the CVE-2023-46604 vulnerability.
Recommendations:
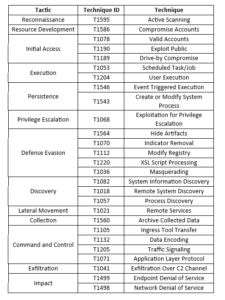
Threat Profile:
References:
The following reports contain further technical details:
https://thehackernews.com/2023/11/gotitan-botnet-spotted-exploiting.html
[/emaillocker]