
EXECUTIVE SUMMARY:
A recent investigation by researchers has unveiled a sophisticated, multi-year campaign targeting end-of-life small home/small office (SOHO) routers and IoT devices. This campaign revolves around an updated version of the notorious "TheMoon" malware. The malware, which had been relatively dormant, has resurfaced to power the growth of a cybercriminal-focused proxy service named Faceless. Researchers have mapped the logical structure of the Faceless proxy service, revealing its alarming expansion and association with other botnets like SolarMarker and IcedID. The widespread use of TheMoon as a supplier of bots to Faceless underscores the severity and sophistication of this threat.[/subscribe_to_unlock_form]
EXECUTIVE SUMMARY:
A recent investigation by researchers has unveiled a sophisticated, multi-year campaign targeting end-of-life small home/small office (SOHO) routers and IoT devices. This campaign revolves around an updated version of the notorious "TheMoon" malware. The malware, which had been relatively dormant, has resurfaced to power the growth of a cybercriminal-focused proxy service named Faceless. Researchers have mapped the logical structure of the Faceless proxy service, revealing its alarming expansion and association with other botnets like SolarMarker and IcedID. The widespread use of TheMoon as a supplier of bots to Faceless underscores the severity and sophistication of this threat.[emaillocker id="1283"]
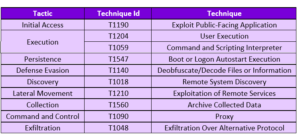
The malware analysis reveals a complex infection process wherein victim devices are first targeted with lightweight loader files. These files decrypt and execute subsequent payloads, including modules responsible for worm-like behavior and proxying internet traffic on behalf of users. The Moon C2 orchestrates the distribution of these malicious payloads, establishing connections with infected devices and facilitating the download of additional modules. Notably, there's a significant overlap between TheMoon and Faceless activity clusters, indicating a symbiotic relationship between the two. The Faceless proxy service operates through a network of compromised IoT devices, offering users anonymity and facilitating criminal activities through obfuscation.
The emergence of this sophisticated campaign underscores the evolving tactics of cybercriminals in leveraging residential proxy services for anonymity and obfuscation. With a growing trend towards bypassing conventional detection methods, such as geolocation-based blocking, the threat landscape continues to evolve. Researchers remains committed to monitoring and mitigating such threats, collaborating with the security community, and employing proactive measures to safeguard the integrity of the internet.
THREAT PROFILE:
REFERENCES:
The following reports contain further technical details:
[/emaillocker]